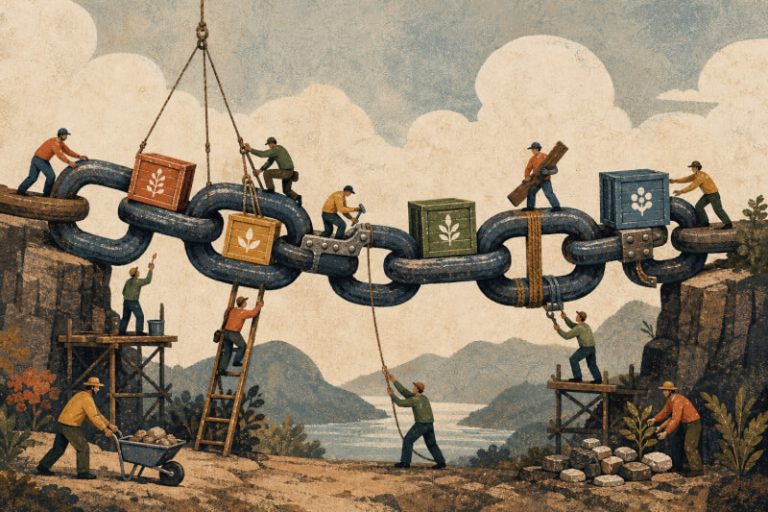
A single weak supplier can disrupt operations, expose sensitive data, and create legal fallout long before an internal security team detects a problem. That is what makes Thrid-Party Risk more than a procurement concern. It now sits at the intersection of cybersecurity, compliance, resilience, and business continuity. For many organizations, the real challenge is not knowing third parties matter. It is understanding how far that risk extends across vendors, service providers, contractors, and partners.
Where the exposure usually begins
Most organizations depend on outside providers to deliver critical services, manage data, support infrastructure, or maintain specialized business systems. That dependence creates efficiency, but it also creates inherited risk. If a third party has weak access controls, poor incident response, or limited visibility into its own subcontractors, the impact can move quickly across the supply chain. In many cases, the organization that suffers the business damage is not the one that caused the security gap.
This is where risk often becomes difficult to manage. Vendor reviews may happen only during onboarding, while the threat landscape keeps changing after contracts are signed. A provider that looked acceptable a year ago may now handle more sensitive information, rely on different subcontractors, or operate in a higher-risk environment. Without continuous review, security teams can end up making decisions based on outdated assumptions.
What businesses often underestimate
Third-party incidents are rarely just technical events. They can delay service delivery, interrupt customer experience, trigger regulatory reporting, and damage commercial relationships. In regulated sectors, they may also raise questions about governance and due diligence. That is why vendor risk should not sit only with IT or procurement. It needs shared ownership across security, legal, compliance, operations, and leadership.
Another common mistake is treating all vendors the same. Not every third party needs the same level of scrutiny. A low-impact supplier does not present the same exposure as a cloud provider, payment processor, or managed service partner with privileged access. Stronger programs classify vendors by business criticality, data sensitivity, and access level so that review efforts focus where the risk is highest.
What a practical third-party risk strategy looks like
An effective approach starts with visibility. Organizations need a clear inventory of third parties, what systems or data they can access, and how essential they are to operations. From there, assessment becomes more meaningful. Rather than relying only on questionnaires, mature programs combine contractual controls, policy reviews, security validation, and ongoing monitoring.
- Rank vendors based on business impact and access risk
- Review security controls before onboarding and throughout the relationship
- Define incident notification and response expectations in contracts
- Monitor changes in vendor posture, ownership, and subcontractor use
- Align procurement, compliance, and security teams around shared criteria
This kind of structure helps organizations move from reactive reviews to ongoing risk management. It also improves decision-making. When leaders can see which external relationships create the most exposure, they can allocate resources more effectively and reduce the chance of a surprise incident.
From vendor oversight to business resilience
Third-party risk management works best when it supports broader business goals. The objective is not to eliminate vendor relationships. It is to build confidence that external dependencies are understood, governed, and aligned with the organization’s risk tolerance. That matters not only for security, but also for audit readiness, operational continuity, and strategic planning.
Organizations evaluating technologies and frameworks for third-party risk can work with Terrabyte to identify solutions that fit their operating model, compliance needs, and supply chain exposure. As a cybersecurity distributor and trusted technology partner, Terrabyte helps businesses compare the right approaches for stronger oversight and more resilient vendor risk management.